Master Compliance.
Minimize Risk.
Observeri is a cybersecurity GRC platform and enterprise GRC solution: AI-powered governance with integrated risk management software, cyber risk management platform telemetry, and IT risk management software workflows that compress audit cycles—without another shelf-ware risk and compliance system.

Compliance Score
94.7%
Active Controls
1,247
Risk Items
23
SOC 2 Certified
ISO 27001 Ready
AI Model Risk Management
Govern every AI model before risk becomes regulation.
AI is moving faster than most governance teams can keep up. From generative copilots and fine-tuned LLMs to autonomous agents and embedded models, every new deployment introduces model risk, bias exposure, data leakage, and compliance uncertainty. If you cannot see how an AI model is built, trained, hosted, and used, you cannot protect the business from it.
AI Model Risk Management on Observeri GRC gives CISOs, AI risk officers, and compliance teams a single system of record for model discovery, risk tiering, acceptable use policy, bias and explainability guardrails, third-party model vendor oversight, and continuous monitoring against frameworks such as the EU AI Act, NIST AI RMF, and ISO/IEC 42001.
Placeholder announcement — full AI Model Risk Management capabilities launching soon on Observeri GRC.
The shift is urgent
77%
of organizations say generative AI models they use are already in production without formal risk governance or model oversight in place.
- Model inventory & risk tiering
- Bias, explainability & drift guardrails
- EU AI Act, NIST AI RMF, ISO 42001 alignment
AI Model Risk Management at a glance
Model inventory
Discover and register every internal, third-party, and open-source model in one place.
Risk-based controls
Map each model to acceptable use, data lineage, safety tests, and approval gates.
Continuous monitoring
Track drift, incidents, and policy changes with AI risk scores tied to the GRC register.
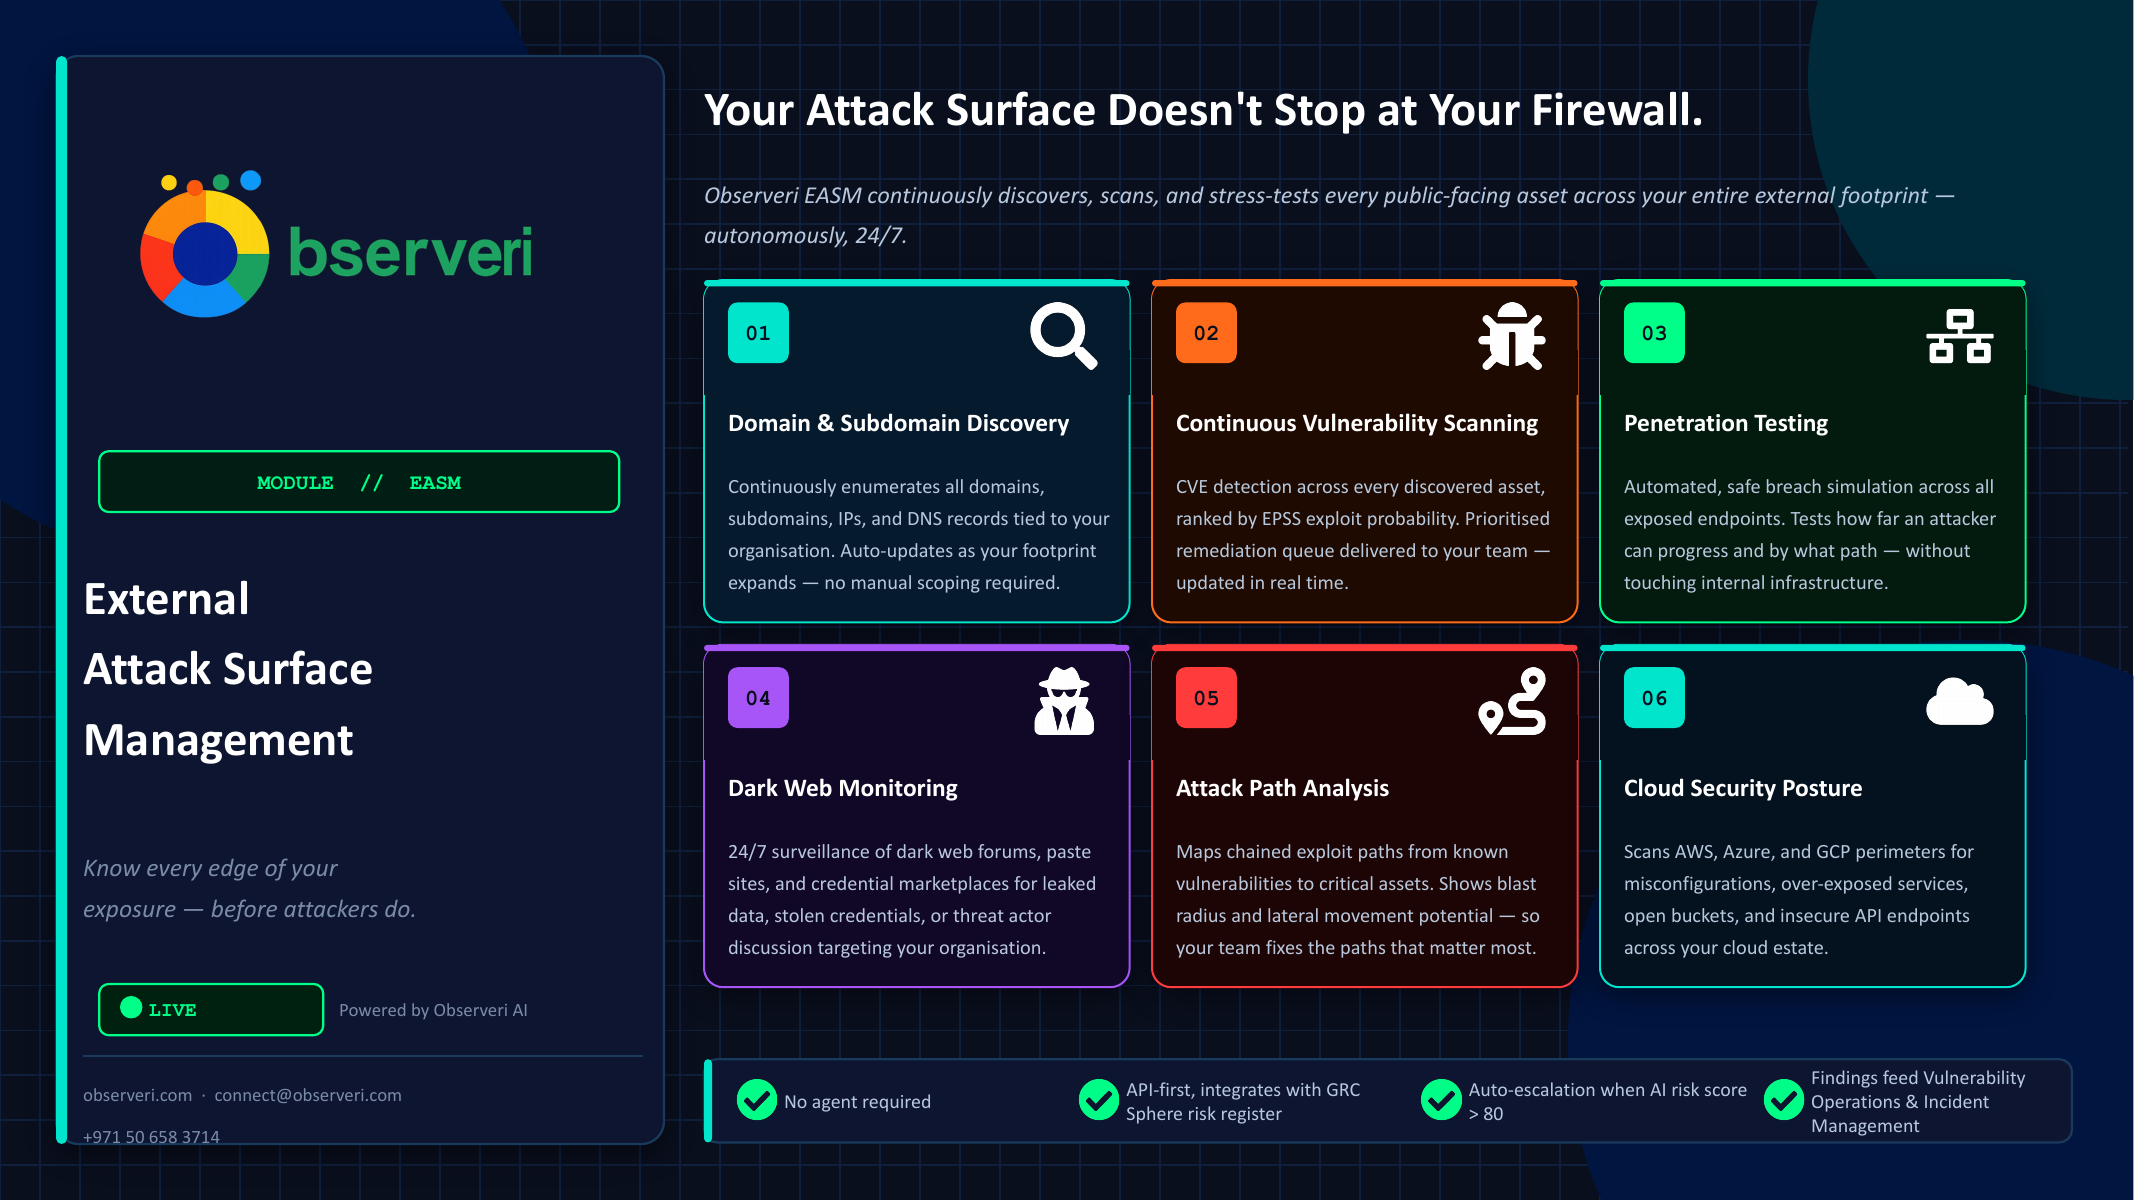
External Attack Surface Management
Know every edge of your exposure — before attackers do.
External Attack Surface Management (EASM) continuously maps everything your organization exposes to the internet—domains, subdomains, cloud services, APIs, and forgotten assets outside the firewall. Observeri discovers, monitors, and prioritizes that footprint so security and GRC teams can close gaps before they become incidents.
For most modern enterprises, the “known” perimeter is a myth. Shadow IT, dormant subdomains, and unsanctioned SaaS expand faster than manual inventories can track. If you don't know an asset exists, you cannot protect it—which is why continuous EASM is now a strategic pillar of resilience on Observeri GRC.
Placeholder announcement — full EASM capabilities launching soon on Observeri GRC.
The reality is stark
70%
of organizations report at least one cyber-attack originating from an unknown or unmanaged internet-facing asset.
- Domain & subdomain discovery
- Vulnerability scanning & dark web monitoring
- Findings tied to GRC risk workflows
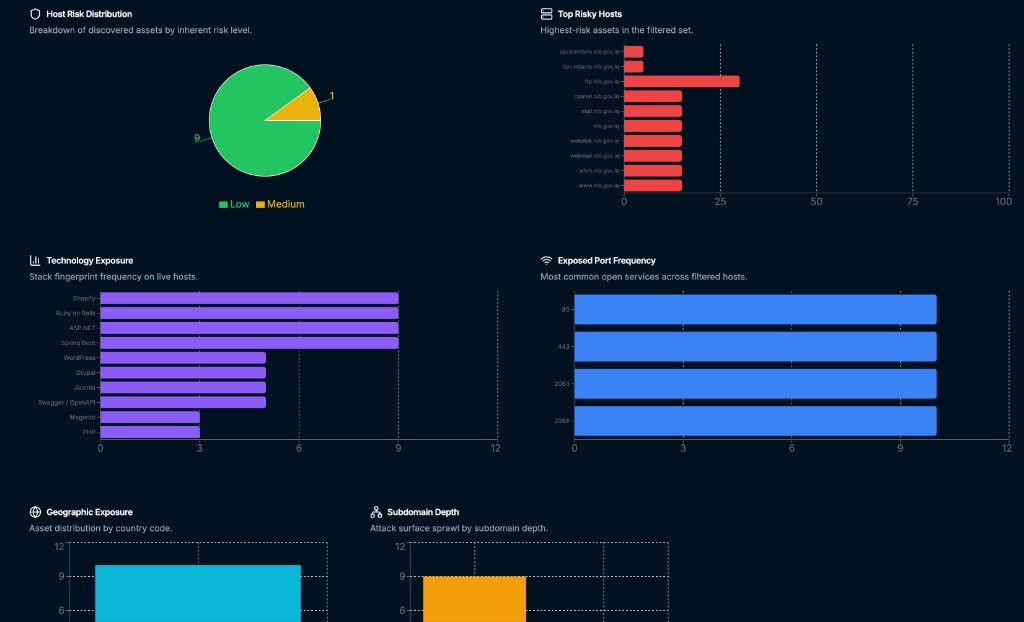
EASM module overview
Search what teams ask for
AI-powered GRC with automated cyber risk exposure you can defend in the boardroom.
Observeri is built as a modern, cost-effective AI cybersecurity GRC solution—continuously mapping controls and evidence to how regulators and investors actually read risk, not just how tickets get closed.
Industries
Vertical programs when you need cybersecurity GRC tailored to operating reality—not generic templates.
Regulation-ready
Map ISO 27001 compliance software, NIST CSF risk management tool, SOC 2 compliance platform, GDPR compliance software, HIPAA compliance management system, and PCI DSS compliance solution work into one regulatory compliance management software spine—plus MiCA, NESA, SAMA, and DORA programs—with audit management software GRC workflows, compliance tracking platform views, and internal audit software tasks tied to live tests.
Replacing legacy GRC
Teams compare Observeri as a MetricStream alternative, ServiceNow GRC alternative, RSA Archer alternative, LogicGate alternative, OneTrust GRC alternative, CyberArrow alternative, or Vanta alternative when they need automation, quantified risk, and faster assurance cycles in one integrated cybersecurity GRC platform.
How buyers use Observeri
- How to prioritize cyber risk and vulnerabilities
- Use vulnerability risk prioritization and business context so fixes follow dollars, exploitability, and control gaps—not noise in the queue.
- How to quantify cyber risk
- Express exposure with risk quantification software and FAIR-style views—annual loss expectancy software metrics and financial cyber risk assessment narratives leadership can budget against.
- How to implement a GRC framework
- Start with scope, control baseline, and evidence automation; keep owners, tests, and policies in one governance risk and compliance software system so implementation survives the first audit.
- Risk vs compliance difference
- Compliance proves you meet obligations; risk management prioritizes what could still hurt the business. Observeri links both so security compliance management software and cyber risk management platform data tell the same story.
- GRC software comparison and demo requests
- Evaluate best GRC software for enterprises on a GRC demo request: time-to-value, AI depth, continuous monitoring, and whether the operational risk management platform actually reduces manual hours.
Financial Impact Analysis
One prevented breach changes the economics immediately.
Observeri GRC’s core argument is simple: mitigation costs roughly 4-6% of recovery exposure, creating 12-27X ROI potential in year one.
Cost of Recovery
Total exposure
$8M - $18.5M
Cost of Mitigation
Total investment
$170K - $400K
Bottom Line Verdict
12-27X ROI in year one
Year 1 benefits in the deck total $9.66M against a modeled $550K investment, with ROI becoming positive within the first month of deployment.
Net Year 1 ROI
$9.11M
Operational Efficiency
Move the team from spreadsheet chasing to strategic action.
Automation ROI
$735K
Direct labor cost saved annually by reducing manual GRC work and audit prep.
Decision Velocity
10-15X
Move from 4-7 week GRC cycles to 2-3 day executive decision windows.
Risk Reduction
83%
Reduce expected annual loss from $12.4M to $2.1M with quantified action plans.
Decision Velocity
From 4-7 weeks to 2-3 days
The PPT positions speed as a competitive moat. Real-time alerts, AI risk analysis, and immediate executive visibility compress the traditional cycle into a faster operating rhythm.
Traditional cycle
4-7 Weeks
Data aggregation, analysis, alignment, and implementation run in serial.
AI-powered cycle
2-3 Days
Alerts in under an hour, AI analysis within hours, and resolution in 48-72 hours.
Executive Value
CEO
Reputation protection, strategic visibility, investor confidence.
CFO
Cost predictability, budget optimization, reduced insurance premiums.
CIO
IT and security alignment, technology ROI, clear modernization roadmap.
CISO
Proactive posture, team efficiency, and stronger board credibility.
Risk Quantification
Speak the CFO's language with expected annual loss.
Instead of abstract red-yellow-green scoring, Observeri GRC reframes exposure in dollars: asset value multiplied by threat probability and residual risk becomes financial impact leadership can budget against.
Quantification Model
Patient Database Server
Real-world before and after
Before
EAL exposure
$1.76M
After Observeri
EAL exposure
$144K
Portfolio view, trend analysis, and board reporting all become easier when security risk is translated into financial exposure instead of technical counts.
Executive Dashboard Preview
Real-time visibility tailored to each decision-maker.
The deck shows dashboards customized by role. The homepage now previews that same idea: executives don't see the same screen, they see the same truth through the lens they own.
CEO
Enterprise Risk Pulse
72
Overall risk score, down 18 points
CFO
Financial Risk Exposure
$2.1M
Expected annual loss, down from $12.4M
CIO
Technology Asset Health
99.8%
Uptime with 100% API health visibility
Board
Governance Summary
Top 5%
Industry benchmark leadership view
Strategic Differentiators
Why Observeri feels different from legacy GRC.
Predictive, Not Reactive
Traditional: Backward-looking audits and after-the-fact reporting.
Observeri: AI predicts breaches 30-90 days before occurrence.
Quantified, Not Theatrical
Traditional: High / medium / low ratings with little board meaning.
Observeri: Expected annual loss expressed in clear financial exposure.
Automated, Not Administrative
Traditional: Manual documentation, spreadsheets, and follow-up loops.
Observeri: 60% workflow automation with AI agents driving remediation.
Integrated, Not Siloed
Traditional: Disconnected tools for assets, threats, and compliance.
Observeri: Unified platform with API-first data flowing into one view.
Healthcare-Proven, Not Generic
Traditional: One-size-fits-all compliance templates.
Observeri: Built around HIPAA, HITRUST, and healthcare risk patterns.
90-Day Roadmap
Fast time-to-value without changing your stack.
The deck promises minimal disruption: SaaS delivery, API-first integration, no extra headcount, and only four hours of executive training. The page now makes that rollout story tangible.
Platform license
$250K - $450K
Implementation
$50K - $100K
ROI breakeven
21 - 30 Days
Days 1 - 30
Foundation
Asset discovery, classification, integrations, and first-pass AI risk calibration.
Quick Win 1
Executive risk dashboard live in 2 weeks.
Days 31 - 60
Activation
Automated assessments, AI remediation workflows, and HIPAA / HITRUST mapping go live.
Quick Win 2
First predicted threat prevented automatically.
Days 61 - 90
Optimization
Governance workflows mature, predictive analytics tune to noise, and board reporting becomes continuous.
Quick Win 3
First audit cycle completed with zero findings.
Can you afford to leave $2M+ of monthly risk exposure unmanaged?
Observeri GRC closes with an investment decision, not a feature checklist: modeled annual cost of $500K, year 1 return above $9M, and a payback period of 21 days.
Annual cost
$500K
Year 1 return
$9M+
Payback
21 Days
Strategic value
Reputation Protection
Executive Briefing
60 minutes
Personalized risk assessment, ROI model, and live executive dashboard walkthrough.
Proof-of-Value
30 days, real environment
Quantified baseline, real insights, and measurable 30-day risk reduction metrics.
Strategic Planning
Board-ready support
Implementation roadmap, budget justification, and leadership alignment materials.
Enterprise GRC & AI risk topics
How teams discover an integrated risk management and compliance platform
“Organizations don’t suffer from lack of data—they suffer from lack of clarity.”
Cybersecurity GRC platform for the full risk and compliance system
Observeri is built as a cybersecurity GRC platform and GRC software cybersecurity teams can run daily—not only at audit time. The same enterprise GRC solution connects governance risk and compliance software workflows with integrated risk management software so finance, IT, security, and legal share one risk and compliance system. Customers consolidate IT risk management software, security compliance management software, and operational risk management platform reporting instead of reconciling spreadsheets across portals.
AI GRC platform with predictive cyber risk analytics
As an AI GRC platform, Observeri layers intelligent risk scoring, automated risk assessment software, and AI compliance automation on top of unified data. Teams get predictive cyber risk analytics, a continuous risk monitoring system, and AI-driven compliance platform cadence without losing defensible evidence. Risk quantification software outputs pair with executive narrative so boards see cyber risk exposure platform metrics they can trust.
Cybersecurity risk management: vulnerability tracking, prioritization, and quantification
Security buyers use Observeri as cybersecurity risk management software that unifies vulnerability tracking, vulnerability prioritization, and vulnerability risk prioritization tooling with cyber risk dashboard software and attack surface risk management platform telemetry. Continuous attack surface management, external attack surface monitoring, and continuous threat exposure management connect discovered assets to live risk scores. Threat monitoring, threat feeds, and vulnerabilities data feed prioritization queues, while dark web monitoring extends visibility beyond the perimeter. AI risk assessment and cybersecurity risk quantification outputs—including FAIR risk analysis and FAIR risk assessment views—help teams prioritize fixes by business impact. Third party cyber risk management, vendor risk cybersecurity platform scoring, and security risk assessment tools feed a cyber risk scoring platform aligned to security posture management GRC practices—so remediation queues match business consequence, not only CVSS.
Compliance & audit: ISO 27001, NIST CSF, SOC 2, GDPR, HIPAA, PCI DSS, SWIFT, MiCA, NESA, NIA, DORA
Regulatory compliance management software in Observeri supports ISO 27001 and ISO27001 compliance software patterns, NIST CSF and NIST 800-53 risk management tool mappings, SOC 2 compliance platform evidence, GDPR compliance software operations, HIPAA compliance and HIPAA compliance management system controls, PCI DSS and PCI compliance solution traceability, SWIFT CSP compliance for financial messaging security, and regional frameworks including MiCA compliance, NESA compliance framework, NIA compliance, SAMA cybersecurity framework, CBUAE compliance, and DORA compliance for operational resilience. Audit management software GRC workflows, compliance tracking platform status, and internal audit software tasks stay linked to live control tests and policies.
FAIR-aligned cyber risk financial modeling and ROI
For quantitative buyers, Observeri supports FAIR risk quantification software approaches—cyber risk financial modeling, annual loss expectancy software views, risk exposure calculation tooling, and quantitative risk analysis platform dashboards. Financial cyber risk assessment and cyber risk ROI platform storylines help CFOs compare control investments to expected loss reduction using transparent assumptions.
Best GRC software for enterprises, UAE / Middle East, banks, and fintech
Teams comparing the best GRC software for enterprises or top cybersecurity GRC platforms start with a GRC software comparison on architecture, automation depth, and time-to-value. Observeri is a strong GRC solution for fintech and GRC tools for banks, with regional relevance as GRC software UAE teams deploy for cybersecurity GRC Dubai, Abu Dhabi compliance software needs, fintech GRC UAE programs, and broader risk management platform Middle East requirements. Ready to buy GRC software? Request a GRC demo and evaluate enterprise risk management tools side-by-side with legacy suites.
Alternatives to MetricStream, ServiceNow GRC, Archer, LogicGate, OneTrust
If you are evaluating a MetricStream alternative, ServiceNow GRC alternative, RSA Archer alternative, LogicGate alternative, or OneTrust GRC alternative, Observeri emphasizes faster deployment, AI-guided prioritization, and quantified cyber exposure without forcing a rip-and-replace on day one.
Problem-led discovery: prioritize risk, implement GRC, automate compliance
Content and in-product guidance answer how to prioritize cyber risk, how to quantify cyber risk, how to implement GRC framework steps, risk vs compliance difference education, cyber risk dashboard examples, challenges in GRC implementation, how to automate compliance, and risk scoring models in cybersecurity—so practitioners and assistants surface Observeri when questions are phrased in natural language.
Long-tail coverage: real-time dashboards, FAIR, continuous monitoring
Observeri maps to searches for an AI-based cyber risk prioritization platform, real-time GRC dashboard for enterprises, automated ISO 27001 risk assessment tool outputs, enterprise cyber risk exposure analytics, continuous compliance monitoring software, integrated GRC platform with AI insights, cyber risk quantification using FAIR model methods, continuous attack surface management, external attack surface monitoring, continuous threat exposure management, threat monitoring software, threat feeds integration, vulnerabilities management, dark web monitoring, and SaaS GRC platform for fintech companies that need rapid onboarding.
Feature-led journeys: registers, controls, audits, vendors, BC
Product teams map capabilities to risk register software, control assessment platform automation, audit workflow automation, policy management software, incident management GRC, third party risk management software, business continuity planning software, and vendor risk assessment tool integrations—so each capability page reinforces how Observeri operationalizes governance end-to-end.
Frequently asked questions
We've compiled answers to the questions we hear most frequently from our community.
Get in touch
Have a question or want a demo? Send us a message and we'll respond within one business day.