Exposure Management
See your full exposure. Close it with precision.
Observeri Exposure Management unifies assessment planning, centralized issue tracking, a dedicated remediation hub, external attack surface visibility, and AI-powered threat analysis—so teams plan tests, prioritize findings, and reduce exposure from the perimeter to the core.
360°
Exposure visibility
AI
Threat & risk priority
SLA
Tracked remediation
Why it matters
Exposure is managed in fragments—not as a programme
Assessments planned in spreadsheets
Security and risk assessments are scheduled manually with no tie to automated compliance testing—so coverage gaps appear only when auditors arrive.
Issues scattered across tools
Audit findings, security assessment results, and compliance deficiencies live in different systems—with no unified queue, risk priority, or SLA enforcement.
Remediation without a command center
Fixes are tracked in email threads and ticket backlogs instead of a dedicated hub with ownership, evidence, and measurable closure against exposure reduction.
External exposure stays invisible
Attack surface changes—new subdomains, exposed services, misconfigurations—go undetected until threat actors or researchers find them first.
What it is
End-to-end exposure reduction from plan to proof
Exposure Management is Observeri's operational layer for reducing cyber exposure across the enterprise. Five integrated sub-modules connect assessment planning and automated compliance testing to centralized issue tracking, SLA-driven prioritization, a dedicated remediation hub, external attack surface management, and AI analysis of emerging threats.
Assessment Planning
Plan security and risk assessments on configurable schedules, trigger automated compliance control tests, and align assessment cadence to frameworks—ISO 27001, SOC 2, NIST, and more—without manual calendar management.
Issues Hub
Centralize audit, security, and compliance issues in one workspace with AI risk prioritization, configurable SLAs, aging alerts, and clear ownership—replacing fragmented finding trackers.
Remediation Hub
A dedicated remediation command center to track fixes from assignment through evidence-based closure—linking every remediation to the exposure it reduces and the SLA it must meet.
Attack Surface Management
Discover and monitor your external attack surface—domains, subdomains, exposed services, and misconfigurations—with continuous visibility into what adversaries can see from outside your perimeter.
Threats Management
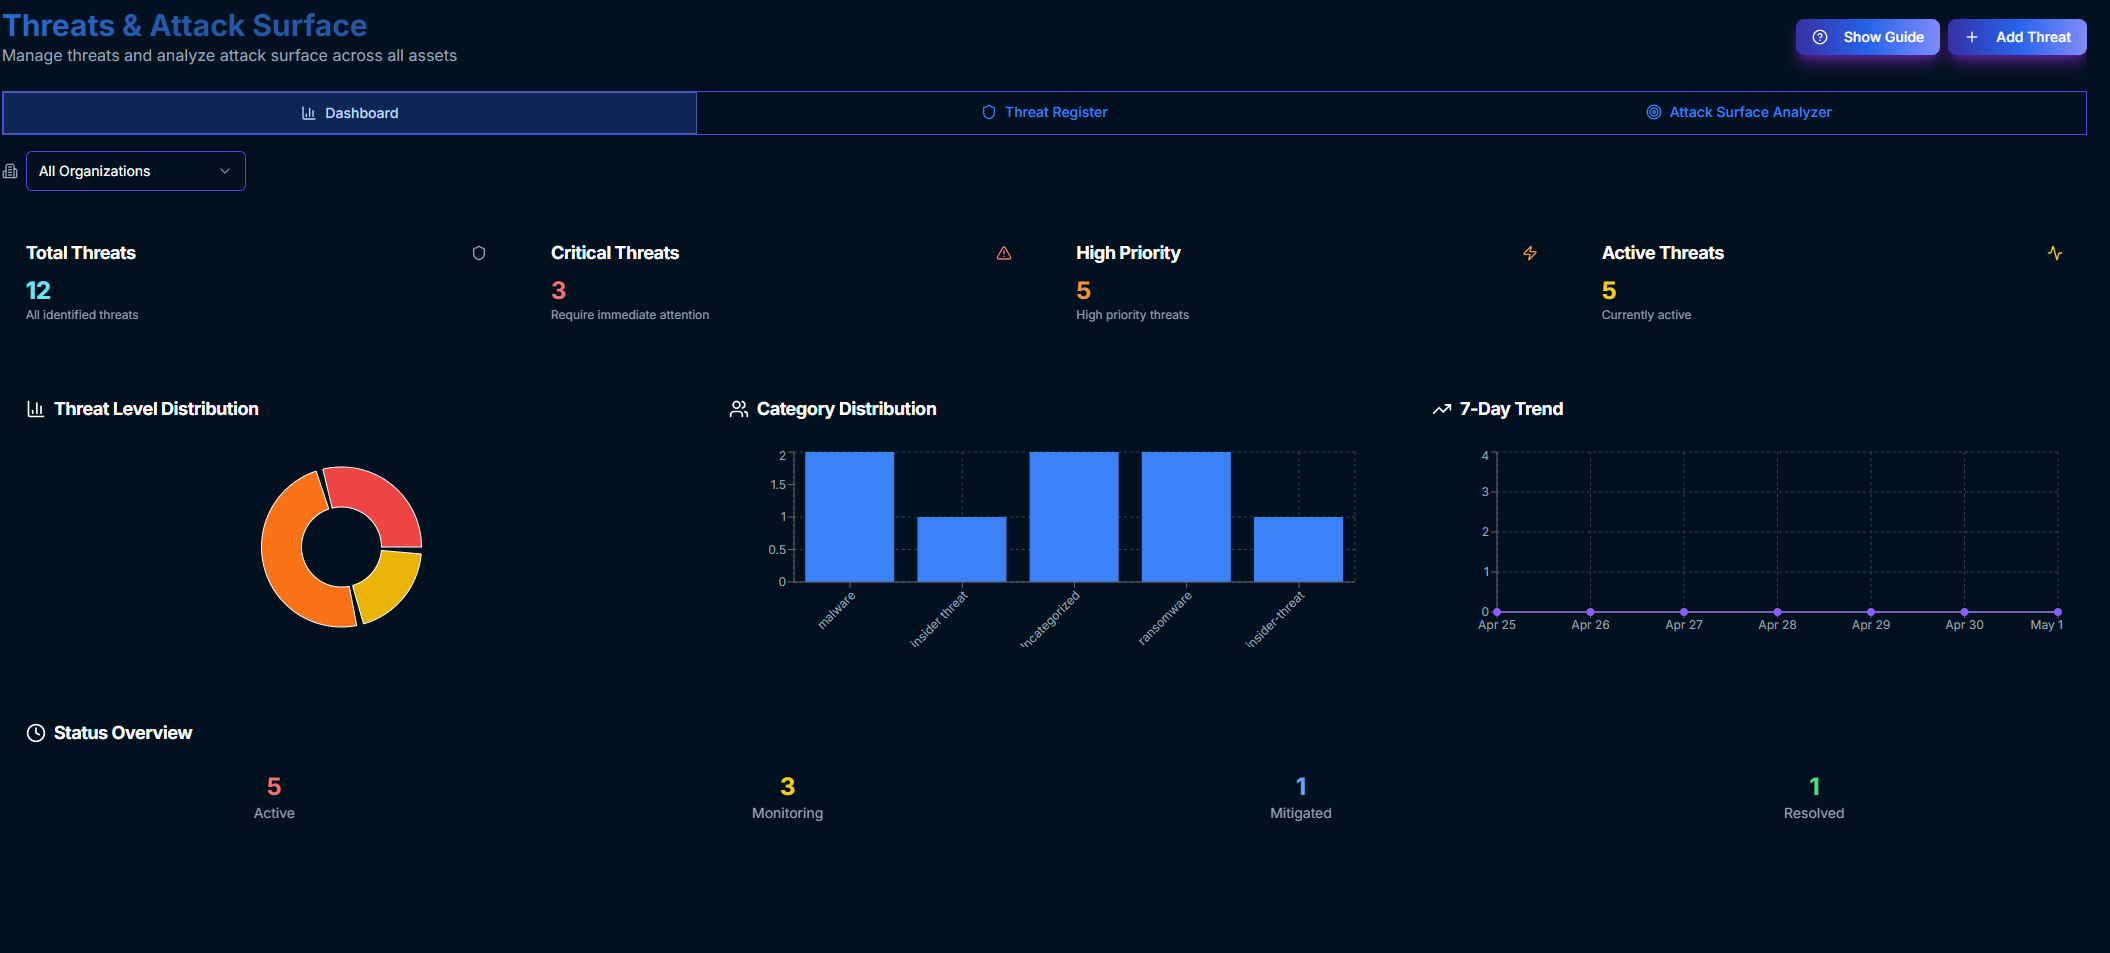
Run AI-powered threat analysis on emerging threats, correlate actors and campaigns to your assets, and prioritize response based on what is actively targeting your industry and technology stack.
Plan with automation
Track with priority
Close with evidence
How it works
Plan. Detect. Prioritize. Remediate. Monitor.
A continuous exposure reduction loop—from automated assessment planning through centralized remediation and live attack surface and threat monitoring.
Step 1
Plan
Schedule assessments and automated compliance tests
Define your security and risk assessment programme—framework scope, control test schedules, and assessment ownership. Observeri triggers automated compliance testing on cadence and routes results directly into the issues hub.
Activities
Platform features
Five sub-modules. One exposure programme.
Automated compliance testing
Schedule and run automated control tests against your compliance frameworks—feeding failures directly into the issues hub with evidence attached.
Unified issues register
Audit, security assessment, compliance, and external findings consolidate into one prioritized queue—eliminating duplicate trackers and conflicting severities.
SLA-driven issue management
Define remediation SLAs by severity, source, and framework. Track aging, send breach alerts, and expose SLA performance to leadership dashboards.
Dedicated remediation hub
Manage every fix from triage to verified closure in a purpose-built workspace—with milestones, evidence, and linkage to exposure reduction metrics.
External attack surface management
Continuously discover and monitor externally visible assets, services, and misconfigurations—closing the gap between internal inventory and internet-facing reality.
AI emerging threat analysis
Observeri AI analyzes threat feeds, actor campaigns, and industry-specific attack patterns—correlating emerging threats to your assets and prioritizing defensive response.
Benefits for your organization
Reduce exposure with a programme teams can run every day
One programme for the full exposure lifecycle
From assessment planning through remediation and continuous monitoring—teams work in a single exposure management programme instead of juggling disconnected tools and spreadsheets.
Prioritize what reduces exposure fastest
AI risk scoring and SLA enforcement ensure the highest-consequence audit, security, and compliance issues get remediated first—protecting crown-jewel assets under pressure.
Prove closure with evidence, not status updates
The remediation hub requires verified evidence before closure—giving auditors and leadership defensible proof that exposure was actually reduced.
See what attackers see before they act
External attack surface management and AI threat analysis keep teams ahead of newly exposed services and emerging adversary activity—closing the outer layer of defence proactively.
Faster path from finding to verified fix
Centralized issues, SLA tracking, and a dedicated remediation hub compress the time from discovery to evidence-based closure—without handoffs lost between audit, security, and ops teams.
Assessment coverage you can defend
Automated compliance testing and scheduled assessments produce a continuous evidence trail—so regulators and auditors see a programme that runs between formal review cycles.
Exposure reduction leadership can measure
Remediation hub metrics, SLA adherence, and attack surface trend data give CISOs and boards quantified proof of exposure reduction—not just ticket volume.
Platform capabilities
Enterprise exposure management, end to end
- Security and risk assessment planning with framework-aligned scoping and scheduling
- Automated compliance control testing with scheduled cadence and evidence capture
- Centralized audit, security, and compliance issues register with deduplication
- AI risk prioritization scoring by impact, exploitability, asset tier, and threat context
- Configurable remediation SLAs by severity, assessment type, and compliance framework
- SLA aging dashboards with near-breach and overdue automated notifications
- Dedicated remediation hub with ownership, milestones, and evidence-based closure
- External attack surface discovery and continuous monitoring of internet-facing assets
- Threat register with actor, campaign, and indicator tracking
- AI-powered emerging threat analysis correlated to asset inventory and industry context
- Integration with AI Risk Operations Center for live asset risk score updates
- Executive exposure dashboards combining issues, remediation, ASM, and threat posture
Quantified outcomes
80%
Faster issue prioritization
5
Integrated sub-modules
100%
SLA-tracked remediations
24/7
Attack surface monitoring
Connected to Observeri GRC
Exposure Management integrates with the AI Risk Operations Center, Vulnerability Operations, and Compliance Management—so every remediated issue updates asset risk scores and reduces enterprise exposure in real time.
Manage exposure from assessment to verified closure
Plan tests, track issues with SLAs, remediate in a dedicated hub, monitor your attack surface, and stay ahead of emerging threats—all in one exposure programme.